

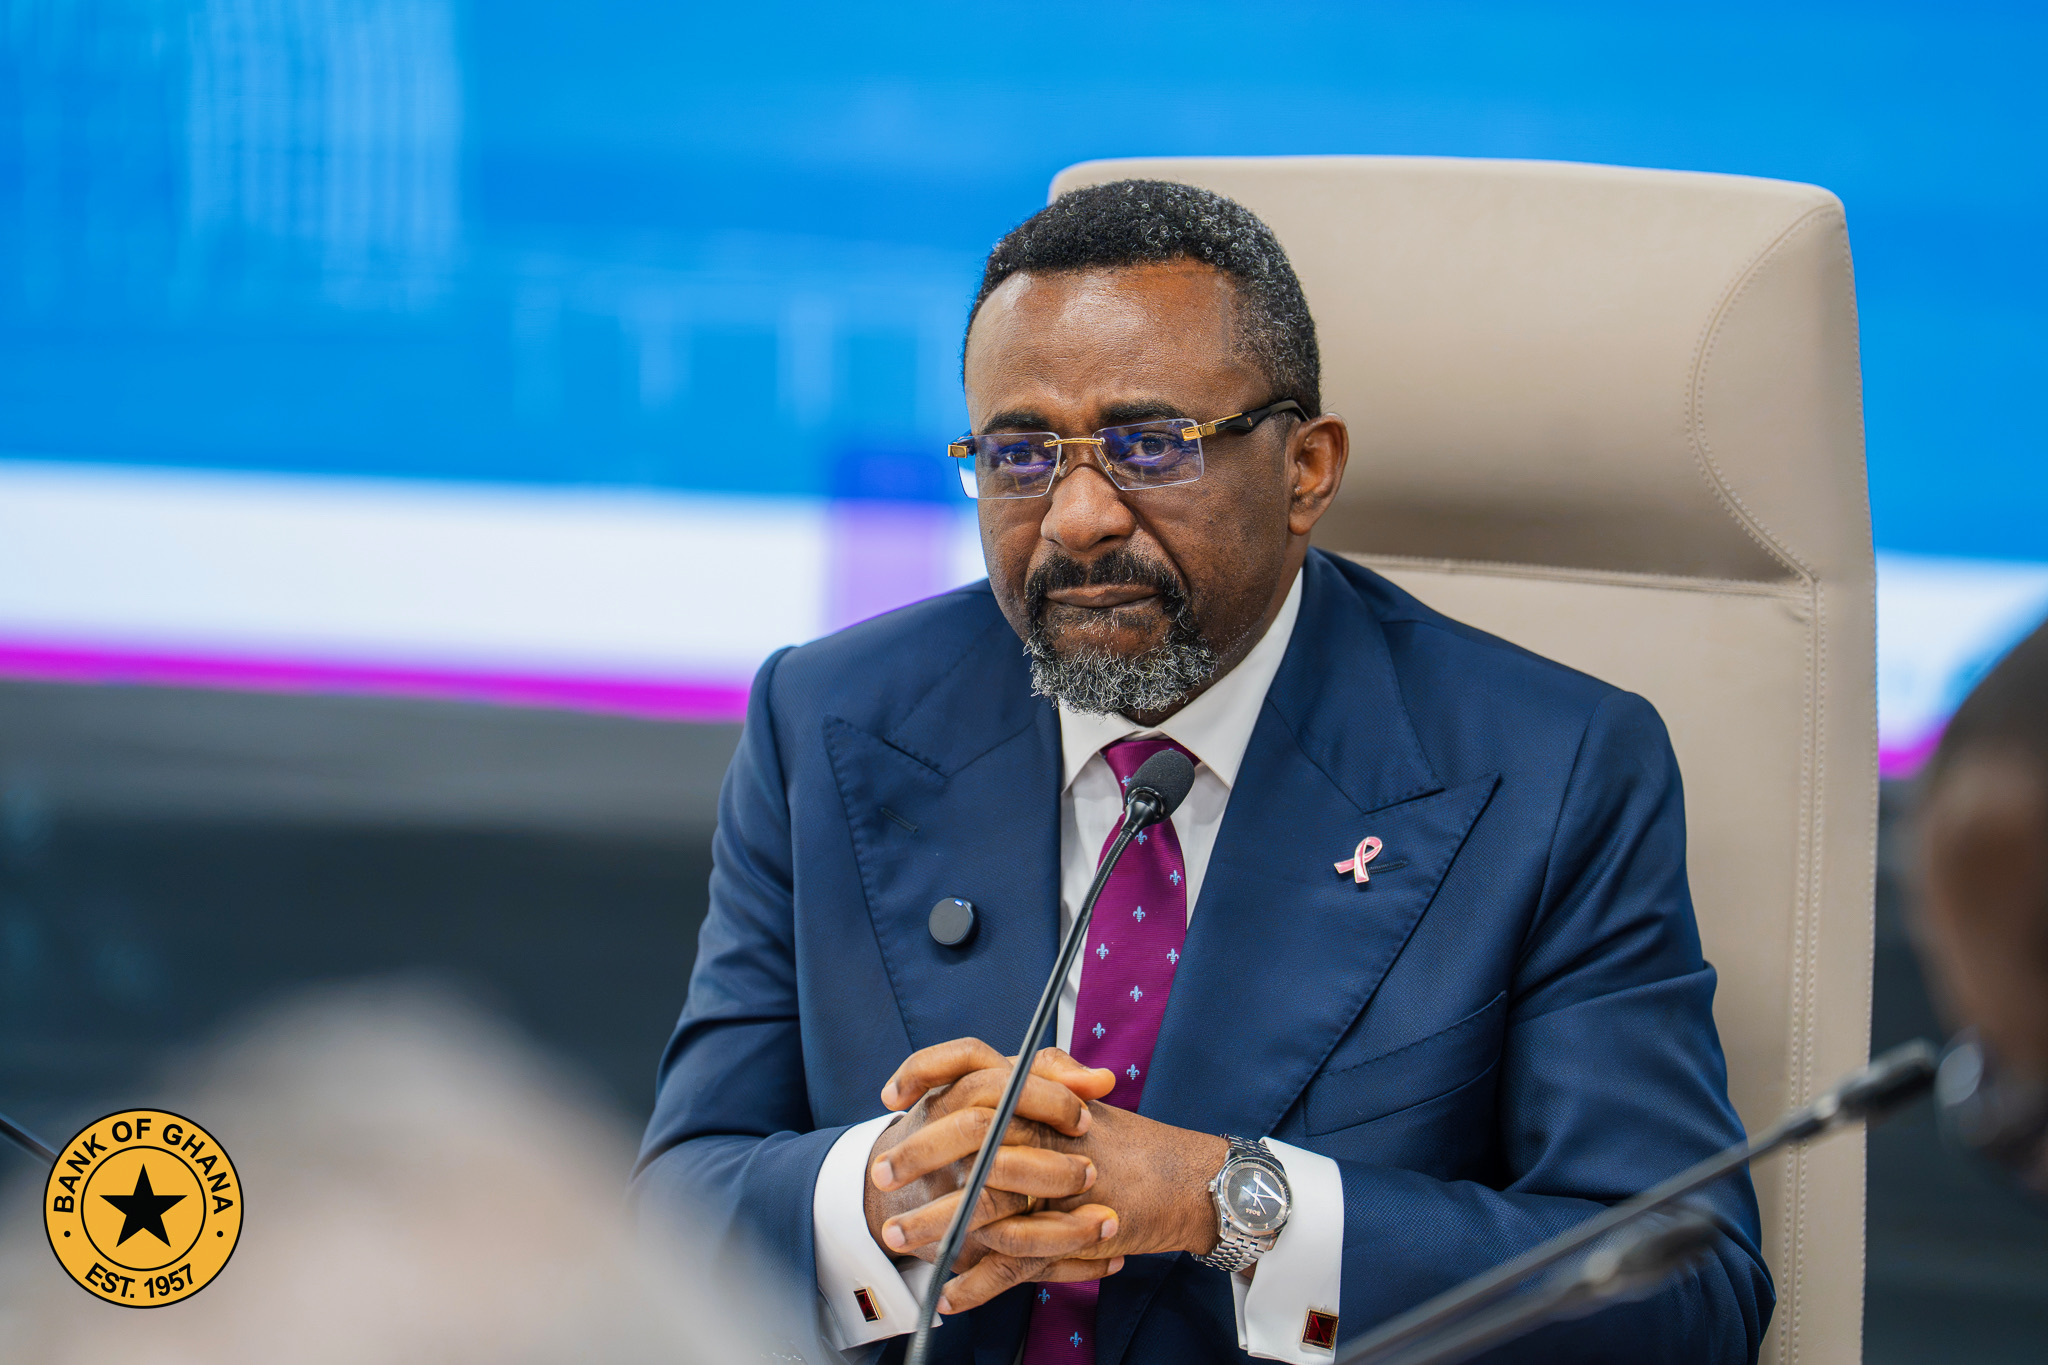

- Fraud Officers Must Have Direct Access to Bank CEOs — Governor Asiama
The Bank of Ghana has directed commercial banks to ensure that their fraud-management functions have direct and unrestricted access to managing directors and chief executives, as the regulator tightens its response to financial crime and governance weaknesses.
Governor Dr Johnson Pandit Asiama said the organisational positioning of fraud units must protect their independence and allow serious concerns to reach the highest decision-making level without interference.
“We urge banks to strengthen their fraud risk management through effective policies and controls to prevent, detect and deter fraud,” he said.
“The fraud function should be appropriately positioned, with direct and unrestricted access to the Managing Director or Chief Executive Officer, to ensure its independence and effectiveness.”
Dr Asiama issued the directive during a post-Monetary Policy Committee engagement with chief executives and heads of banks at the Bank of Ghana headquarters in Accra.
The intervention follows concerns raised by the Ghana Association of Banks over the different positions assigned to fraud functions across financial institutions.
While some banks operate specialised and independent fraud units, others place the responsibility within compliance, risk, internal audit, security or operational departments. Such variations can affect reporting authority, access to information and the ability of officers to investigate senior personnel or commercially sensitive transactions.
Direct access to the chief executive is intended to reduce the risk that fraud warnings are diluted, delayed or suppressed as they move through multiple layers of management.
“Fraud is a significant risk that requires our serious attention,” Dr Asiama said.
He directed banks to ensure that officers responsible for fraud prevention and investigation possess the necessary skills, professional certifications and technical competence.
The directive signals that the central bank increasingly regards fraud management as a governance issue rather than merely an operational or security function.
A fraud unit may have sophisticated monitoring tools but remain ineffective if its officers lack authority, independence or access to senior decision-makers.
Giving the function direct access to a chief executive could improve the speed at which banks respond to internal collusion, cyber-enabled fraud, identity theft, suspicious transfers and misconduct involving employees or third-party service providers.
The reporting arrangement will, however, need strong safeguards to prevent chief executives themselves from becoming the final gatekeepers of sensitive investigations.
Effective governance would require fraud units to have additional access to board-level risk or audit committees, particularly where allegations involve senior executives.
Banks would also need clear procedures protecting investigators and whistleblowers from retaliation.
The directive comes as Ghana’s financial system becomes increasingly dependent on mobile money, digital banking, payment-service providers and third-party technology companies.
Digitalisation has lowered transaction costs and widened access to financial services, but it has also expanded the channels through which fraud can occur.
The Bank of Ghana is consequently strengthening supervisory expectations around cybersecurity, customer-fund protection and third-party risk.
It is also working with financial institutions to implement its Cyber and Information Security Directive and develop further guidance for regulated payment-service providers operating within corporate groups.
The regulator is separately intensifying efforts against illegal digital-credit providers and reviewing the safeguards governing Ghana’s rapidly expanding digital-payments ecosystem.
The focus on fraud forms part of a broader regulatory programme covering credit risk, liquidity and technology.
The Bank of Ghana plans to introduce a Credit Risk Management Directive governing loan origination, monitoring and recovery as private-sector credit expands rapidly.
It will also issue a Liquidity Coverage Ratio Directive requiring banks to maintain sufficient high-quality liquid assets to withstand a severe 30-day liquidity shock.
For banks, the message is that stronger profitability and credit growth must be accompanied by tighter internal controls.
The direct reporting requirement may appear to be a change in organisational structure, but its effectiveness will ultimately be measured by whether banks detect fraud earlier, protect customers more effectively and impose accountability regardless of the seniority of those involved.

